Does Your Business Meet NHS Cyber Security Requirements?
Healthcare organisations and businesses supplying services to the NHS need to take cyber security seriously because a security incident can affect far more than business operations. It can expose sensitive patient information, disrupt essential services and create risks across the wider healthcare supply chain. The specific requirements an organisation needs to meet depend on its
October 8, 2026-
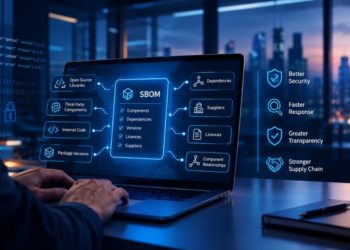
Does Your Business Need a Software Bill of Materials (SBOM)?
Yes. A Software Bill of Materials (SBOM) is not currently mandatory for every UK business, but it is becoming an important part of software supply chain security. An SBOM provides a structured inventory of the components used within an application, helping organisations identify vulnerable dependencies, investigate security issues and respond more quickly when new vulnerabilities
October 7, 2026 -
What Should UK Businesses Do After the Megalodon Supply Chain Attack?
The Megalodon supply chain attack showed how attackers can compromise software development environments without directly attacking a company’s production systems. In May 2026, malicious GitHub Actions workflows were injected into thousands of repositories, allowing attackers to target CI/CD environments and attempt to steal cloud credentials, tokens, SSH keys and other sensitive information. For UK businesses
October 6, 2026 -
Should UK businesses move from passwords to passkeys?
Yes, UK businesses should begin moving towards passkeys, but a phased approach is more practical than trying to eliminate passwords immediately. Legacy applications, third-party systems and some recovery processes may still require passwords, so organisations need a transition strategy that supports both methods. Passwords remain a common authentication method, but phishing, password reuse, credential stuffing
September 30, 2026