
Does Your Business Need a Software Bill of Materials (SBOM)?
- October 7, 2026
- Posted by: Gradeon
- Category: Cyber Security
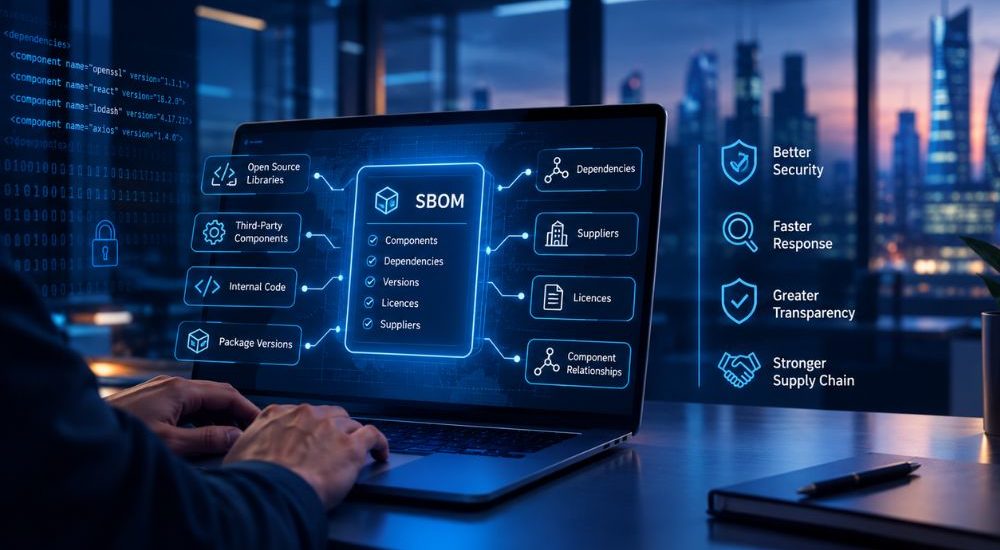
Yes. A Software Bill of Materials (SBOM) is not currently mandatory for every UK business, but it is becoming an important part of software supply chain security. An SBOM provides a structured inventory of the components used within an application, helping organisations identify vulnerable dependencies, investigate security issues and respond more quickly when new vulnerabilities are disclosed.
For businesses that develop software, operate SaaS platforms, use open-source components or rely heavily on third-party applications, maintaining an accurate SBOM can provide greater visibility into software risk and support stronger cyber resilience.
What Is a Software Bill of Materials?
A Software Bill of Materials is a structured inventory of the software components used to build an application.
It is similar to an ingredients list on a food product. Instead of listing food ingredients, an SBOM identifies the libraries, packages, frameworks and other components that make up a software application.
Depending on the organisation and the SBOM standard being used, the inventory may include:
- Open-source libraries.
- Third-party software components.
- Internal code modules.
- Component versions.
- Software suppliers.
- Dependency relationships.
- Identifiers associated with software components.
This information gives security and development teams a clearer understanding of what software they are running and where individual components originate.
Why Are SBOMs Becoming More Important?
Modern software rarely consists entirely of code developed internally.
Applications often depend on open-source libraries, third-party packages, cloud services and external components. These dependencies help organisations develop and release software faster, but they also introduce risks that can be difficult to identify without proper visibility.
If a vulnerability is discovered in a widely used software component, an organisation needs to know whether that component exists within its applications.
Without an accurate inventory, security teams may have to search through multiple applications and repositories manually. An up-to-date SBOM can make this process significantly more efficient.
This is particularly relevant as the wider cyber threat landscape continues to evolve, with attackers increasingly targeting trusted suppliers, software components and connected technology environments.
What Are the Benefits of Using an SBOM?
An SBOM does not prevent a cyber attack by itself. Its value comes from improving visibility and helping businesses make faster, better-informed security decisions.
Improve software visibility
Many organisations do not have complete visibility into every software component used across their applications.
An SBOM provides a structured record that can help businesses understand:
- Which components are being used.
- Which versions are installed.
- Which applications depend on specific components.
- Which suppliers provide those components.
- Where vulnerable components may exist.
Better visibility gives security and development teams a clearer picture of the organisation’s software supply chain.
Respond faster to newly discovered vulnerabilities
When a serious vulnerability is disclosed, one of the first questions a business needs to answer is whether it is affected.
For example, if a vulnerability is discovered in a widely used open-source library, organisations need to identify which applications contain that library and which versions are installed.
With an up-to-date SBOM, businesses can more quickly:
- Identify potentially affected applications.
- Locate vulnerable components.
- Prioritise remediation.
- Assess potential business impact.
- Communicate with relevant stakeholders.
This can reduce the time between vulnerability disclosure and remediation.
Strengthen software supply chain security
Software supply chain attacks can exploit trusted components and development processes rather than attacking an organisation directly.
An SBOM gives businesses greater visibility into the components entering their software environment. This can support dependency monitoring, supplier reviews and vulnerability management.
However, an SBOM should be considered one part of a wider software security programme rather than a standalone security control.
Should Every UK Business Have an SBOM?
Not necessarily.
The value of an SBOM depends on the organisation’s software environment, risk profile and role within the technology supply chain.
An SBOM is particularly useful for businesses that:
- Develop customer-facing applications.
- Build or distribute software products.
- Operate SaaS platforms.
- Use significant numbers of open-source dependencies.
- Maintain complex applications.
- Operate DevOps or CI/CD environments.
- Supply software to larger organisations.
- Work with customers that require software security assurance.
A business that develops a relatively small internal application may have different requirements from a SaaS provider whose software is used by thousands of customers.
The important question is not simply whether an organisation has an SBOM. It is whether the organisation has sufficient visibility into the software components that could create security or operational risk.
When Should a Business Create an SBOM?
Businesses should consider generating an SBOM during the software development lifecycle rather than creating one manually after an incident occurs.
Ideally, SBOM generation should be integrated into the build and release process so that each software version can be associated with an accurate component inventory.
This is particularly useful when applications change frequently because dependencies may be added, removed or updated between releases.
Automating the process can help reduce the risk of an SBOM becoming outdated.
What Information Should an SBOM Contain?
The exact information can vary depending on the format and requirements of the organisation.
A useful SBOM should provide enough information to identify software components and understand their relationships within an application.
Depending on the implementation, this can include:
- Component name.
- Version.
- Supplier or origin.
- Unique component identifiers.
- Dependency relationships.
- Package information.
- Licence information where relevant.
The purpose is to make the software inventory useful to security, development, procurement and risk teams rather than treating it simply as a technical document.
How Should Businesses Manage SBOMs?
Creating an SBOM is only the first step. Its value depends on how accurately it is maintained and how the information is used.
Businesses should consider:
- Generating SBOMs automatically during software builds.
- Updating the inventory whenever dependencies change.
- Linking SBOMs to specific application versions.
- Monitoring components for newly disclosed vulnerabilities.
- Reviewing third-party dependencies regularly.
- Restricting access to sensitive software inventory information.
- Retaining relevant SBOM records alongside release documentation.
Businesses should also include software components within their wider vulnerability management processes.
A software vulnerability assessment can help identify weaknesses across applications and infrastructure, while an SBOM provides visibility into the components that make up those applications. These approaches can therefore complement each other rather than replace one another.
What Are the Challenges of Implementing an SBOM?
Although SBOMs can improve software visibility, implementing them across a complex environment can create practical challenges.
Common issues include:
- Large numbers of software dependencies.
- Legacy applications with limited documentation.
- Frequently changing dependencies.
- Different SBOM formats and tooling.
- Difficulty integrating SBOM generation into existing pipelines.
- Incomplete information about third-party components.
- Keeping inventories accurate after every release.
For this reason, organisations should avoid treating an SBOM as a one-time compliance exercise.
Automating generation and integrating it into existing development processes is generally more sustainable than asking teams to manually maintain spreadsheets or documents.
Can an SBOM Help During a Cyber Incident?
Yes.
An accurate SBOM can help security teams determine whether an affected component is present within their environment following a newly disclosed vulnerability or software supply chain incident.
For example, if a widely used dependency is found to contain a critical vulnerability, the organisation can use its software inventory to identify potentially affected applications and prioritise investigation.
However, an SBOM does not tell an organisation whether an application has actually been exploited. Additional investigation, monitoring and security testing may still be required.
Businesses should also consider how their incident response teams would use software inventory information during an actual incident.
Including a software supply chain scenario in cyber incident response exercises can help teams practise identifying affected systems, coordinating technical investigations and making business decisions under pressure.
How Does an SBOM Support Third-Party Risk Management?
An SBOM can also provide useful information when businesses depend on external software suppliers.
Before adopting a critical application or software product, organisations may want to understand what components are included, how those components are maintained and how vulnerabilities are handled.
This can support wider supplier due diligence and help businesses ask more informed security questions during procurement.
For organisations with a large number of technology suppliers, software component visibility can form part of a broader third-party risk management programme.
However, businesses should not assume that receiving an SBOM automatically means that a supplier’s software is secure. The information still needs to be assessed alongside vulnerability management, security testing, supplier controls and incident response arrangements.
Does an SBOM Improve Cyber Security?
An SBOM can improve cyber security by providing greater visibility into software composition, but it is not a security control that prevents attacks on its own.
Its main value is helping organisations understand what software they use and respond more efficiently when vulnerabilities or supply chain risks emerge.
An effective approach combines SBOM management with:
- Secure software development.
- Dependency management.
- Vulnerability monitoring.
- Access control.
- Application security testing.
- Supplier risk management.
- Incident response planning.
- Continuous security monitoring.
Businesses should also regularly review whether their applications and supporting environments remain secure as software changes over time.
What Should UK Businesses Do First?
Businesses that do not currently maintain an SBOM do not necessarily need to create an inventory of every application immediately.
A more practical approach is to start with the applications and software components that present the greatest business risk.
Organisations can begin by:
- Identifying critical applications and software products.
- Mapping their key dependencies.
- Selecting an appropriate SBOM generation method.
- Automating SBOM creation within the development process where possible.
- Connecting component information with vulnerability monitoring.
- Defining who is responsible for reviewing and maintaining SBOM information.
- Testing how the information would be used during a security incident.
This approach allows organisations to build software supply chain visibility gradually while focusing resources on their most important systems.
Frequently Asked Questions
Is an SBOM mandatory in the UK?
There is currently no general legal requirement for every UK business to maintain an SBOM. However, requirements can vary by sector, contract and customer. Some organisations may request software component information as part of procurement, security assurance or supplier risk assessments.
Which UK businesses benefit most from an SBOM?
Software developers, SaaS providers, technology companies and organisations that rely heavily on third-party or open-source components can benefit significantly. The value is particularly high where applications are complex or frequently updated.
Does an SBOM prevent software supply chain attacks?
No. An SBOM does not prevent an attacker from compromising a software component or development environment. Its primary benefit is visibility, which can help organisations identify affected components and respond more quickly when a security issue emerges.
How often should an SBOM be updated?
An SBOM should reflect changes to the software it describes. If dependencies or application versions change frequently, the SBOM should be regenerated as part of the software build or release process.
Can an SBOM replace vulnerability management?
No. An SBOM identifies software components, while vulnerability management helps organisations identify, prioritise and remediate security weaknesses. The two processes work best together.
Improving Software Supply Chain Visibility With an SBOM
A Software Bill of Materials can give UK businesses greater visibility into the software components they depend on and help security teams respond more efficiently when vulnerabilities emerge.
It is not a replacement for secure development, vulnerability management or security testing. Instead, it provides an important layer of information that can support these processes.
For organisations developing software or relying heavily on third-party components, the practical starting point is to identify critical applications, understand their dependencies and automate SBOM generation wherever possible.
As software supply chains become increasingly complex, knowing what components are being used is an important part of understanding and managing cyber security risk.
