
How to Conduct a Cyber Tabletop Exercise: A Guide for UK Businesses
- September 21, 2026
- Posted by: Gradeon
- Category: Cyber Security
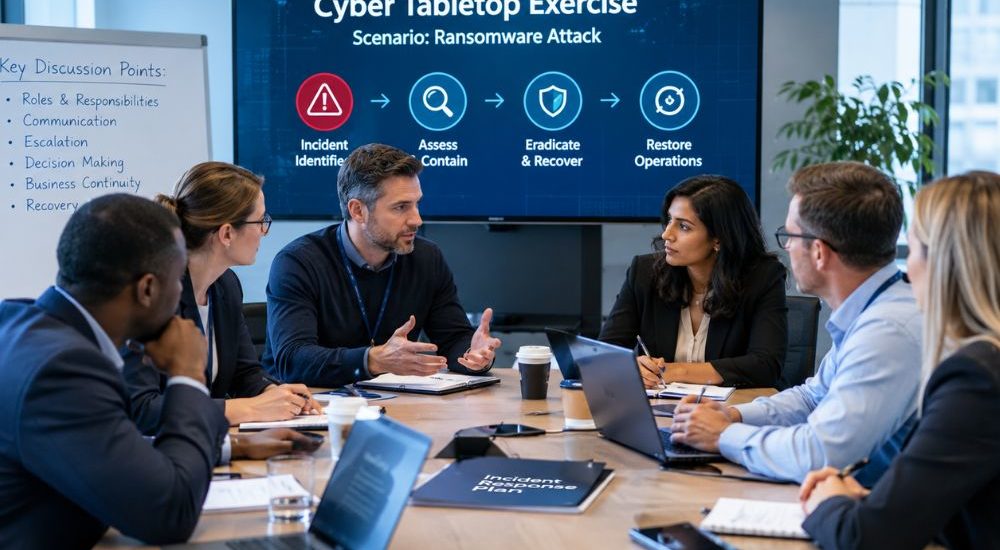
Why should UK businesses conduct cyber tabletop exercises?
Cyber tabletop exercises help UK businesses evaluate how effectively they would respond to a cyber incident before one occurs. By simulating realistic scenarios, organisations can test incident response plans, clarify roles and responsibilities, identify communication gaps and improve decision-making under pressure.
Regular exercising can also help organisations identify weaknesses in their response arrangements and make practical improvements before a real incident creates operational disruption. The NCSC describes cyber incident exercising as a controlled way to practise, evaluate and improve incident response plans.
What is a cyber tabletop exercise?
A cyber tabletop exercise is a discussion-based simulation that allows an organisation to rehearse its response to a cyber security incident in a controlled environment. Rather than testing technical systems directly, participants work through a realistic scenario and discuss the actions they would take at different stages of the incident.
The NCSC defines tabletop exercises as discussion-based sessions where representatives from relevant teams consider their roles, responsibilities, expected activities and key decision points in response to a prepared cyber incident scenario.
These exercises can help organisations evaluate decision-making, communication, escalation procedures and coordination between departments. They can also reveal weaknesses in existing response plans that may otherwise only become apparent during a real incident.
Why tabletop exercises matter
An incident response plan can look effective on paper but still contain practical gaps when different teams need to act under pressure. A tabletop exercise provides an opportunity to test how those arrangements work in practice.
A cyber tabletop exercise can help businesses:
- Validate incident response procedures.
- Improve coordination between departments.
- Identify gaps in decision-making.
- Test internal and external communication processes.
- Review business continuity arrangements.
- Increase confidence among leadership teams.
- Identify areas where additional training may be required.
The purpose is not to produce perfect answers. Instead, the exercise should help the organisation understand what works, what does not and what needs to change.
Who should participate?
Cyber incidents rarely affect only the IT department. A practical response may require decisions from several areas of the organisation, particularly when an incident affects customers, employees, suppliers or business operations.
Depending on the scenario, participants may include:
- Senior management.
- IT and cyber security teams.
- Operations managers.
- HR representatives.
- Legal and compliance teams.
- Communications or public relations staff.
- Business continuity managers.
- Relevant third-party suppliers.
The exact group should reflect the organisation’s structure and the scenario being tested. Including the people who would actually make decisions during an incident makes the exercise more realistic and useful.
How to plan a cyber tabletop exercise
Careful preparation helps ensure that the exercise produces meaningful findings rather than becoming a general discussion about cyber security.
Define the objective
Begin by deciding what the exercise is intended to test.
Objectives might include:
- Testing ransomware response.
- Reviewing communication procedures.
- Assessing executive decision-making.
- Evaluating business continuity arrangements.
- Testing supplier incident management.
- Reviewing escalation and reporting procedures.
A clearly defined objective keeps the exercise focused and makes it easier to identify whether the exercise achieved what it was designed to test.
Choose a realistic scenario
The scenario should reflect the organisation’s risk profile, technology environment and business operations.
Common scenarios include:
- Ransomware attacks.
- Business Email Compromise.
- Data breaches.
- Cloud service outages.
- Insider threats.
- Third-party supplier compromise.
Using a realistic scenario encourages participants to consider practical decisions rather than discussing cyber security only in general terms.
Organisations can also use findings from cyber security vulnerability assessments to help identify technical risks that could inform future exercise scenarios.
Prepare supporting materials
Before the exercise begins, facilitators should prepare:
- The exercise timeline.
- Scenario updates or injects.
- Discussion questions.
- Expected decision points.
- Relevant business documentation.
- Contact and escalation information where appropriate.
The information should be realistic enough for participants to make decisions without turning the exercise into a technical test.
How to run the exercise effectively
A tabletop exercise should encourage structured discussion rather than technical troubleshooting.
The facilitator presents the scenario and introduces new developments as the exercise progresses. Participants then discuss how they would respond based on their existing plans, responsibilities and available information.
During the exercise, participants may need to consider:
- Immediate response actions.
- Roles and responsibilities.
- Internal and external communication.
- Escalation procedures.
- Customer and stakeholder management.
- Legal or regulatory considerations.
- Recovery priorities.
- Supplier or third-party coordination.
The facilitator should record important decisions, areas of uncertainty and points where participants cannot agree on the appropriate course of action. These observations can provide valuable evidence of where the organisation’s response arrangements need improvement.
Evaluate the outcome
The value of a tabletop exercise comes from analysing what happened during the discussion and turning the findings into practical actions.
After the exercise, organisations should review:
- Whether response procedures were understood.
- Any delays in decision-making.
- Communication challenges between teams.
- Gaps in existing policies or procedures.
- Unclear responsibilities or escalation routes.
- Areas requiring additional training.
- Dependencies on suppliers or third parties.
- Actions needed to improve the response plan.
The NCSC recommends using cyber incident exercising as an opportunity to learn and improve organisational resilience rather than treating it as a one-off activity.
Businesses can also review data breach resilience planning to consider how response arrangements can reduce the operational impact of a cyber incident.
Common mistakes to avoid
Tabletop exercises may provide limited value if they are poorly designed or treated simply as a compliance exercise.
Common mistakes include:
- Choosing unrealistic scenarios.
- Excluding important decision-makers.
- Focusing only on technical teams.
- Allowing discussions to become too theoretical.
- Failing to document lessons learned.
- Not assigning responsibility for follow-up actions.
- Failing to update response plans after the exercise.
- Treating the exercise as a one-time activity.
A successful exercise should result in clear observations and practical actions that can be tracked after the session.
How often should businesses conduct tabletop exercises?
There is no single frequency that applies to every organisation. The appropriate approach depends on factors such as the organisation’s risk profile, industry, technology environment, regulatory requirements and the extent to which its operations have changed.
Businesses should consider exercising their response plans regularly and after significant changes that could affect incident response. These might include major technology implementations, changes to suppliers, organisational restructuring or significant changes in the threat environment.
The NCSC’s guidance emphasises making testing and exercising a routine part of cyber resilience rather than relying on a single exercise.
Organisations should also consider whether different scenarios are needed over time. Repeating exactly the same exercise may provide less value than testing different situations that could affect the business.
Make tabletop exercises part of an ongoing resilience programme
A single tabletop exercise cannot prepare an organisation for every possible cyber incident. Businesses should treat exercising as part of a broader approach to cyber resilience and continuously improve their response arrangements based on lessons learned.
Exercises may cover:
- Ransomware attacks.
- Business Email Compromise.
- Supply chain compromises.
- Insider threats.
- Cloud service failures.
- Data breaches.
Regular testing helps organisations keep response procedures familiar and identify changes that may be required as their technology, people and business operations evolve.
Organisations should also review their response plans after significant business changes, technology upgrades, newly identified risks or major incidents. Combining scenario-based exercises with risk assessments and appropriate security testing can provide a more complete view of organisational preparedness.
Frequently asked questions
What is the main purpose of a cyber tabletop exercise?
The main purpose is to allow an organisation to practise and evaluate how it would respond to a cyber incident in a controlled environment. It helps identify weaknesses in response arrangements before a real incident occurs.
Who should facilitate the exercise?
An exercise can be facilitated internally or by an external specialist. The facilitator should guide the discussion, introduce scenario developments and document important decisions and observations without taking over the decision-making process.
Are tabletop exercises only suitable for large organisations?
No. Businesses of different sizes can use tabletop exercises. A smaller organisation may run a relatively simple scenario involving key decision-makers, while a larger organisation may involve multiple departments, suppliers and other stakeholders.
Does a tabletop exercise test technical security controls?
Not directly. A tabletop exercise is primarily discussion-based and focuses on response plans, roles, decisions and coordination. Other forms of security testing may be needed to assess technical controls.
What should happen after a tabletop exercise?
The organisation should document the findings, assign responsibility for corrective actions and update relevant policies or response plans where necessary. Follow-up is important because the main value of an exercise comes from addressing the weaknesses it identifies.
Strengthening Cyber Resilience Through Regular Tabletop Exercises
Cyber tabletop exercises give UK businesses a practical way to evaluate their incident response arrangements without waiting for a real cyber attack. By using realistic scenarios, involving the right decision-makers and documenting lessons learned, organisations can identify gaps in communication, escalation and decision-making.
The most effective approach is to treat exercising as part of an ongoing resilience programme. Businesses should use the findings from each exercise to improve their response plans, strengthen coordination and prepare for the types of incidents that could have the greatest impact on their operations.
Where an organisation experiences or suspects a significant security incident, having appropriate breach support arrangements in place can also help ensure that response activities are coordinated effectively.
